Secure the plant floor without stopping the line.
Close every inbound path into PLCs, HMIs, and plant networks while engineers, OEMs, and your data platforms keep access. Operational in 90 minutes, with no firmware changes.
SEE IT IN YOUR ENVIRONMENT
Connected plants run on equipment that was never built to be connected
For decades, air gaps and a well-guarded perimeter kept production networks safe, and for a plant that only talked to itself, that worked. Today, MES, ERP, cloud analytics, and OEM support all need a line into the same equipment. Every one of those lines is a way in.
Equipment that can't wait for IT's patch cycle. PLCs, RTUs, and HMIs run for decades and can't go offline for an update. Hardening them device by device isn't an option.
Vendor access that never really closes. OEM support, integrators, and contractors connect through VPNs and jump boxes that stay open long after the job is done.
Xiid connects the workspace to approved devices
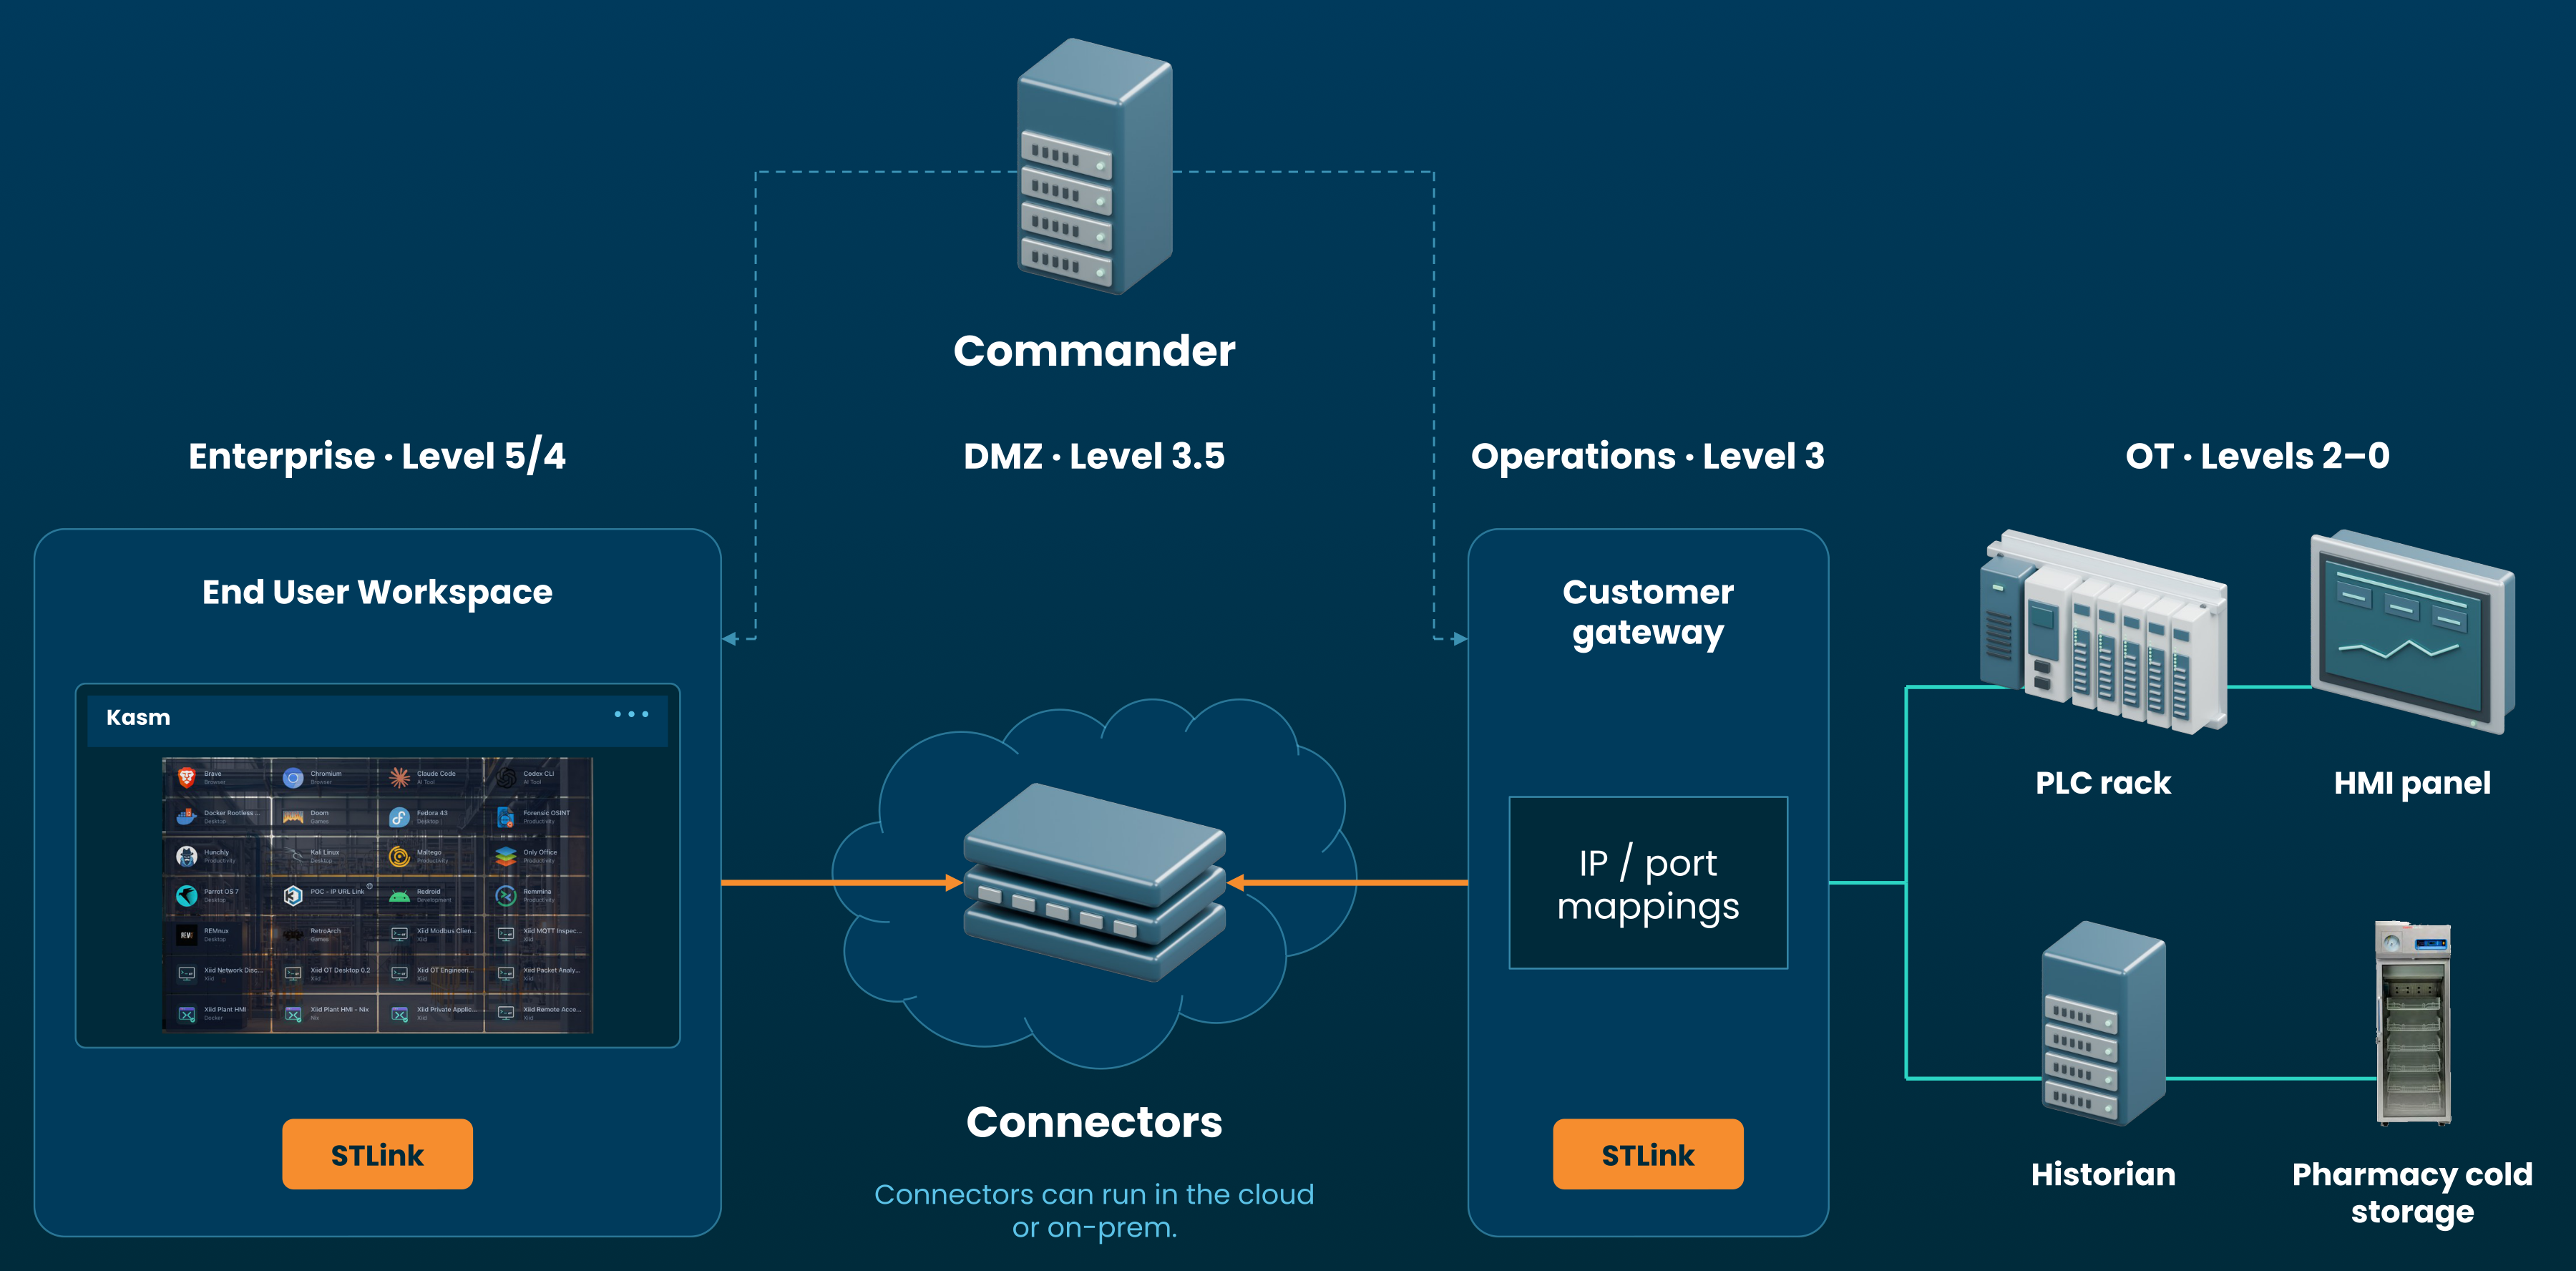
Connection diagram
Every connection your plant needs, nothing an attacker can use
Control networks no scanner can find.
Terniion closes every inbound port on the equipment and its network. PLCs, HMIs, and SCADA servers talk only through outbound-only, process-bound tunnels, so there is nothing to discover from the IT network or the internet.
OEM support without the standing VPN.
Vendors and integrators reach the specific process on the specific machine they're authorized for, only when a session is needed. No jump box, and no view of the network behind it.
A compromised laptop gets nowhere.
Process-level microsegmentation gives every connection its own isolated path. Malware on an engineering workstation has no route into PLCs, safety systems, or the rest of the line.
Plant data out, no opening the plant.
Telemetry, maintenance history, and quality data flow outbound to historians, MES, and AI analytics platforms through triple-encrypted tunnels. The Connector that brokers them never decrypts a byte.
Your line keeps running while security moves in.
Terniion installs alongside what you already run, one site at a time, with each new tunnel live in under 90 seconds.
No firmware changes or device replacement
No shutdown window
No network redesign
Reliable over cellular, satellite, and aging field links
Built to support the frameworks that guide manufacturers
Regulators and insurers now ask the same question: how exposed is your production environment? Terniion gives you a clear answer, backed by closed ports and cryptographic controls you can show an auditor.

IEC 62443. Process-level tunnels act as tightly scoped conduits.
NIST CSF 2.0. No inbound ports, process-level isolation, credential-less access.
CNSA 2.0. Post-quantum encryption for assets that stay in service for decades.
NIS2. Third-party access goes through scoped, auditable tunnels.
The typical arrangement is a jump server or PC stored locally, and all that's doing is moving the attack surface to some remote building.
Tell us what's running on your floor.
We'll show you which paths Terniion closes and how your engineers, vendors, and data platforms keep working